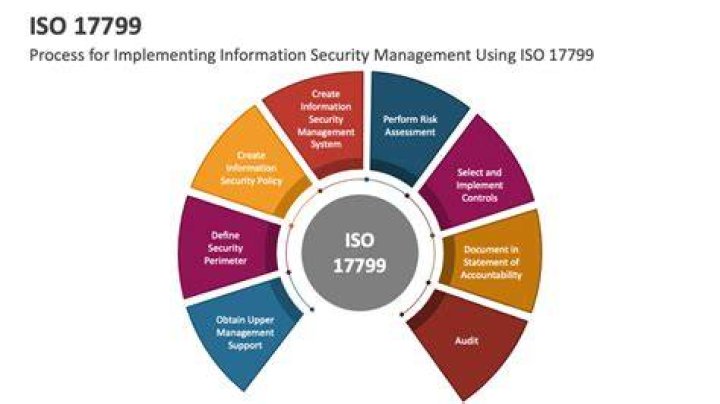
What is the ISO 17799?
 Olivia Carter

.
Keeping this in view, what is ISO in information technology?
ISO/IEC 27002 is an information security standard published by the International Organization for Standardization (ISO) and by the International Electrotechnical Commission (IEC), titled Information technology – Security techniques – Code of practice for information security controls.
Also, what is the difference between ISO 27001 and ISO 27002? The key difference between ISO 27001 and ISO 27002 is that ISO 27002 is designed to use as a reference for selecting security controls within the process of implementing an Information Security Management System (ISMS) based on ISO 27001. Organisations can achieve certification to ISO 27001 but not ISO 27002.
what is the purpose of ISO 27002?
The ISO 27002 standard is a collection of information security guidelines that are intended to help an organization implement, maintain, and improve its information security management.
What is the ISO IEC 27002 standard?
ISO/IEC 27002 is the international standard that outlines best practices for implementing information security controls. ISO/ IEC 27002 is the companion standard for ISO/IEC 27001, the international standard that outlines the specifications for an information security management system (ISMS).
Related Question Answers
Is ISO 17799 still valid?
ISO 17799 Information Security Standard. ISO 17799 is obsolete. Please see ISO IEC 27002 2013. program or improve its current information security practices.How many types of ISO standards are there?
Here are 10 ISO standards and what they mean for your business.- ISO 9000 - Quality Management.
- ISO / IEC 27000 - Information Security Management Systems.
- ISO 14000 – Environmental Management.
- ISO 31000 - Risk Management.
- ISO 50001 - Energy Management.
- ISO 26000 - Social Responsibility.
What is ISO cyber security?
The term ISO/IEC 27032 refers to 'Cybersecurity' or 'Cyberspace security,' which is defined as the protection of privacy, integrity, and accessibility of data information in the Cyberspace.What does ISO IEC stand for?
International Organization for Standardization
What are the IT standards?
Information Technology Standards. Standards are quantifiable metrics to which parties adhere for purposes of allowing some common ground for interchange. Some view monetary systems developed for the exchange of goods as the earliest standards. A language is a standard for communication.How do I get ISO 27000 certified?
ISO 27001 registration/certification in 10 easy steps- Prepare.
- Establish the context, scope, and objectives.
- Establish a management framework.
- Conduct a risk assessment.
- Implement controls to mitigate risks.
- Conduct training.
- Review and update the required documentation.
- Measure, monitor, and review.
What does ISO 27004 describe?
ISO 27004 defines how data should be collected and analyzed, how measurements should be constructed and how the measurement program should be documented and integrated into the ISMS. ( Steffen Weiss, 2005) The standard provides Plan-do-check-act (PDCA) model for measurement of security where.How much does ISO 27001 Cost?
Total cost for ISO 27001 certificate: $48,000.What is ISO 27003?
ISO/IEC 27003:2010 focuses on the critical aspects needed for successful design and implementation of an Information Security Management System (ISMS) in accordance with ISO/IEC 27001:2005. It describes the process of ISMS specification and design from inception to the production of implementation plans.What is ISO 27002 2013?
ISO/IEC 27002:2013 gives guidelines for organizational information security standards and information security management practices including the selection, implementation and management of controls taking into consideration the organization's information security risk environment(s).What are the components of isms?
Major Components of an ISMS- Scope and boundaries.
- Information classification.
- Risk Management Methodology.
- Risk Treatment.
- Statement of Applicability.
- Incident Handling.
- Physical Security.
- Controls that meet the organisation's business activity.