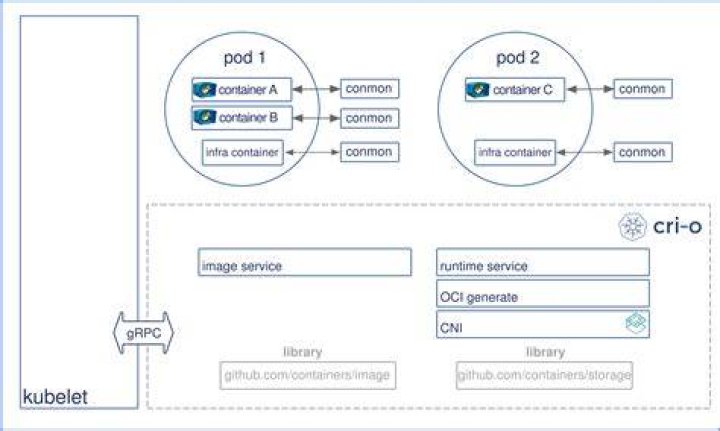
CRI-O is an implementation of the Kubernetes CRI (Container Runtime Interface) to enable using OCI (Open Container Initiative) compatible runtimes. It is a lightweight alternative to using Docker as the runtime for kubernetes..
Also to know is, what does CRI O stand for?
CRI-O: A Lightweight Container Runtime for Kubernetes And that's what CRI-O provides. The name derives from CRI plus Open Container Initiative (OCI), because CRI-O is strictly focused on OCI-compliant runtimes and container images.
Also, what is CRI in Kubernetes? An overview of the Kubernetes Container Runtime Interface (CRI) The CRI is an integration point between Kubernetes and container runtimes that makes pods (groups of containers) work in Kubernetes clusters.
One may also ask, how do you use CRI O?
To set up a CRI-O container engine to use with an OpenShift Container Platform cluster, you can:
- Install CRI-O along with a new OpenShift Container Platform cluster or.
- Add a node to an existing cluster and identify CRI-O as the container engine for that node. Both CRI-O and Docker nodes can exist on the same cluster.
What is container run time?
A container runtime is software that executes containers and manages container images on a node. Today, the most widely known container runtime is Docker, but there are other container runtimes in the ecosystem, such as rkt, containerd, and lxd.
Related Question Answers
Is Docker free to use?
Docker CE is free to use and download. Basic: With Basic Docker EE, you get the Docker platform for certified infrastructure, along with support from Docker Inc. You also gain access to certified Docker Containers and Docker Plugins from Docker Store.What is Docker Linux?
Docker is an open source project that automates the deployment of applications inside Linux Containers, and provides the capability to package an application with its runtime dependencies into a container. It provides a Docker CLI command line tool for the lifecycle management of image-based containers.How do I start Containerd?
Starting containerdYou can download one of the latest source builds for containerd on the Downloads page and then use your favorite process supervisor to get the daemon started. This will extract the containerd source into a containerd-1.3. 2 directory. If you are using systemd, there is a containerd.What is ad container?
D Container is a large corrugated box, aka Gaylord box, they are perfect for shipping, storage, transporting, moving, and more. This D Container bulk cargo box is a Heavy Duty 350# bursting strength Double Wall fiberboard / cardboard box which includes a heat-treated stamped pallet.What is Docker Containerd Shim?
containerd-shimThe shim allows for daemonless containers . According to Michael Crosby it's basically sits as the parent of the container's process to facilitate a few things. First it allows the runtimes, i.e. runc,to exit after it starts the container.Does Docker use runC?
RunC is a container runtime originally developed as part of Docker and later extracted out as a separate open source tool and library. As a “low level” container runtime, runC is mainly used by “high level” container runtimes (e.g. Docker) to spawn and run containers, although it can be used as a stand-alone tool.What are Docker alternatives?
Different Docker Alternatives are as follows: - Virtual Box. The Virtual Box tool by Oracle, as the name suggests, creates a virtual environment which allows a developer to set up and run his applications in different platforms.
- Vagrant.
- Wox.
- Rancher.
- Kubernetes.
- Apache Mesos.
- LXC Linux Container.
Is Docker OCI compliant?
The Open Container Initiative (OCI) is a Linux Foundation project to design open standards for operating-system-level virtualization, most importantly Linux containers. runC was first released in July 2015 as version 0.0. 1 and it is included in RHEL 8.0 as a Docker replacement.Does Kubernetes use Docker?
As Kubernetes is a container orchestrator, it needs a container runtime in order to orchestrate. Kubernetes is most commonly used with Docker, but it can also be used with any container runtime. RunC, cri-o, containerd are other container runtimes that you can deploy with Kubernetes.What is a container image?
A container image is an unchangeable, static file that includes executable code so it can run an isolated process on information technology (IT) infrastructure.What is container runtime interface?
The Container Runtime Interface (CRI) is a plugin interface which enables kubelet to use a wide variety of container runtimes, without the need to recompile. CRI consists of a protocol buffers and gRPC API, and libraries, with additional specifications and tools under active development.What is Docker engine?
Docker Engine supports the tasks and workflows involved to build, ship and run container-based applications. The engine creates a server-side daemon process that hosts images, containers, networks and storage volumes.What is a Cgroup driver?
Cgroup driversWhen systemd is chosen as the init system for a Linux distribution, the init process generates and consumes a root control group ( cgroup ) and acts as a cgroup manager. Systemd has a tight integration with cgroups and will allocate cgroups per process.What are the processes running in a node?
Each node contains the services necessary to run pods and is managed by the master components. The services on a node include the container runtime, kubelet and kube-proxy.What is Cgroup driver in Docker?
detected "cgroupfs" as the Docker cgroup driver. Control groups are used to constrain resources that are allocated to processes. A single cgroup manager will simplify the view of what resources are being allocated and will by default have a more consistent view of the available and in-use resources.What is OpenShift cloud?
Red Hat OpenShift Online (RHOO) is Red Hat's public cloud application development and hosting service which runs on AWS. It can run any Docker-based container, but Openshift Online is limited to running containers that do not require root.What container engine does Kubernetes use?
Google Kubernetes Engine. GKE is an enterprise-grade platform for containerized applications, including stateful and stateless, AI and ML, Linux and Windows, complex and simple web apps, API, and backend services. Leverage industry-first features like four-way auto-scaling and no-stress management.What is POD sandbox change?
Googled that and it seemed that it means that the docker server inside the node was down, restarted and then because the “sandbox changed” it restarted all the pods inside it including our beloved pg main.What is POD sandbox?
When you enable GKE Sandbox on a node pool, a sandbox is created for each Pod running on a node in that node pool. In addition, nodes running sandboxed Pods are prevented from accessing other Google Cloud services or cluster metadata. Note: Pods that do not run in a sandbox are called regular Pods. 
 Ava Hall